It sure looks like hackers breached a major ID card verification
An identity theft search site claimed to have more than 150 million driver's license photos stolen from an ID verification service.
By Dillip Chowdary • Sep 03, 2026 • Source: TechCrunch
What happened
architects who rely on third-party identity verification services to onboard users and validate official government credentials. (100 words)
How it works
* ## What happened Paragraph 1 (80–160 words): An online platform specializing in identity theft search services announced that it had obtained a database containing more than 150 million driver's license photos. According to the claims made by
Advertisement
Tech Pulse Daily
Get tomorrow's pulse first
Join engineers who read Tech Pulse before stand-up. Free, weekday mornings.
Why it matters
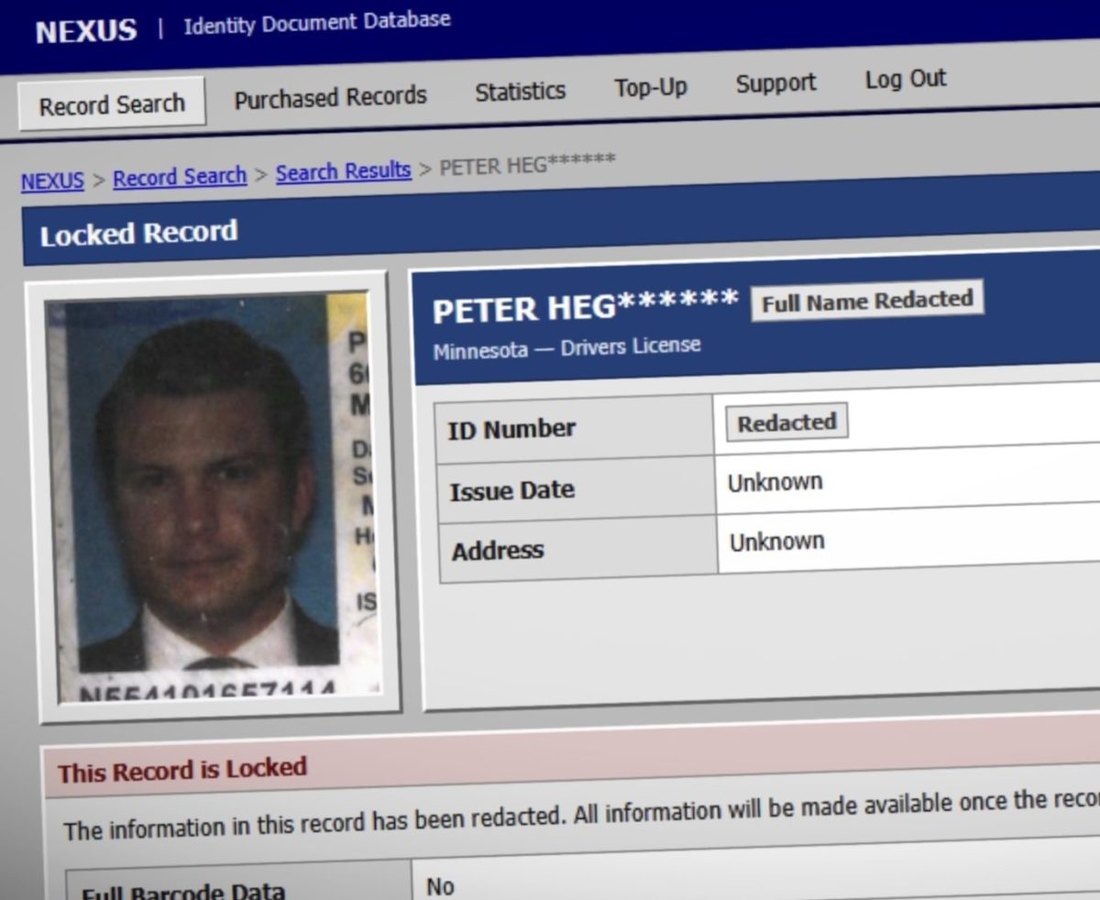
If you have handed over your driver’s license, passport, or other form of identity document to verify your information in the real world, like at a bar, a weed store, or when booking a car rental, there’s a good chance it’s now been stolen in a suspected massive data breach. That’s according to a jaw-dropping report by independent security journalist Brian Krebs, who says a company used to verify government-issued identity documents in the real world was likely hacked and its vast stores of people’s ID cards were exfiltrated.
Who is affected
Krebs reports that an identity theft site called Nexus, which launched on the dark web this week, claimed to allow users to search through more than 150 million driver’s licenses and passports belonging to people who live in the United States and Canada. A post advertising the site on a known Russian cybercrime forum said Nexus added about half a million new documents daily, sourced from a “major identity verification company,” implying that the hackers had near real-time access to the identity verification company’s systems.
What to watch next
The advert claims that “customer photos are displayed if available.” Krebs found that his own driver’s license was among the searchable records in the database, confirming that the data was authentic. See the full write-up from TechCrunch via the source link for quotes and complete context.
Developer Action Items
- ☐ Inventory whether sure looks like hackers runs in prod, CI, staging, or on laptops before you debate severity.
- ☐ Confirm the vendor's fixed build for sure looks like hackers from TechCrunch, then schedule the patch window.
- ☐ If you cannot patch today, isolate the service, rotate tokens that sat on the affected surface, and raise the logging floor.
- ☐ Record the decision and residual risk so the next on-call does not re-litigate whether you are exposed.
- ☐ Treat unexpected emails that mention sure looks like hackers (shipping, invoices, password resets) as phishing until verified.

Author
Dillip Chowdary
Writes Tech Bytes coverage of AI, engineering, and the tools that actually ship. Editor of Tech Pulse Daily.
Related on Tech Bytes
Over 3 Million WordPress Sites Affected by Migration Plugin Vulnerability
Read →
Cisco Warns of Unpatched Secure Email Flaws, Patches Critical Switch Vulnerabilities
Read →
Microsoft Teams, Outlook fail to launch on ARM-based Windows PCs
Read →
Claude Code skill: no emdashes
Read →
Today's Tech Pulse briefing
Full briefing →
Advertisement