Rate limits for private vulnerability reports
Open source maintainers are receiving more low-quality and automated vulnerability reports, which can bury the reports that matter.
By Dillip Chowdary • Oct 02, 2026 • Source: GitHub Changelog
At a glance
- Product
- Private vulnerability reporting
- Limit
- Daily per-user cap on new reports
- Scope
- Applies to your repository and across GitHub
- Message
- Reporters at the limit are asked to retry later
- Custom limit
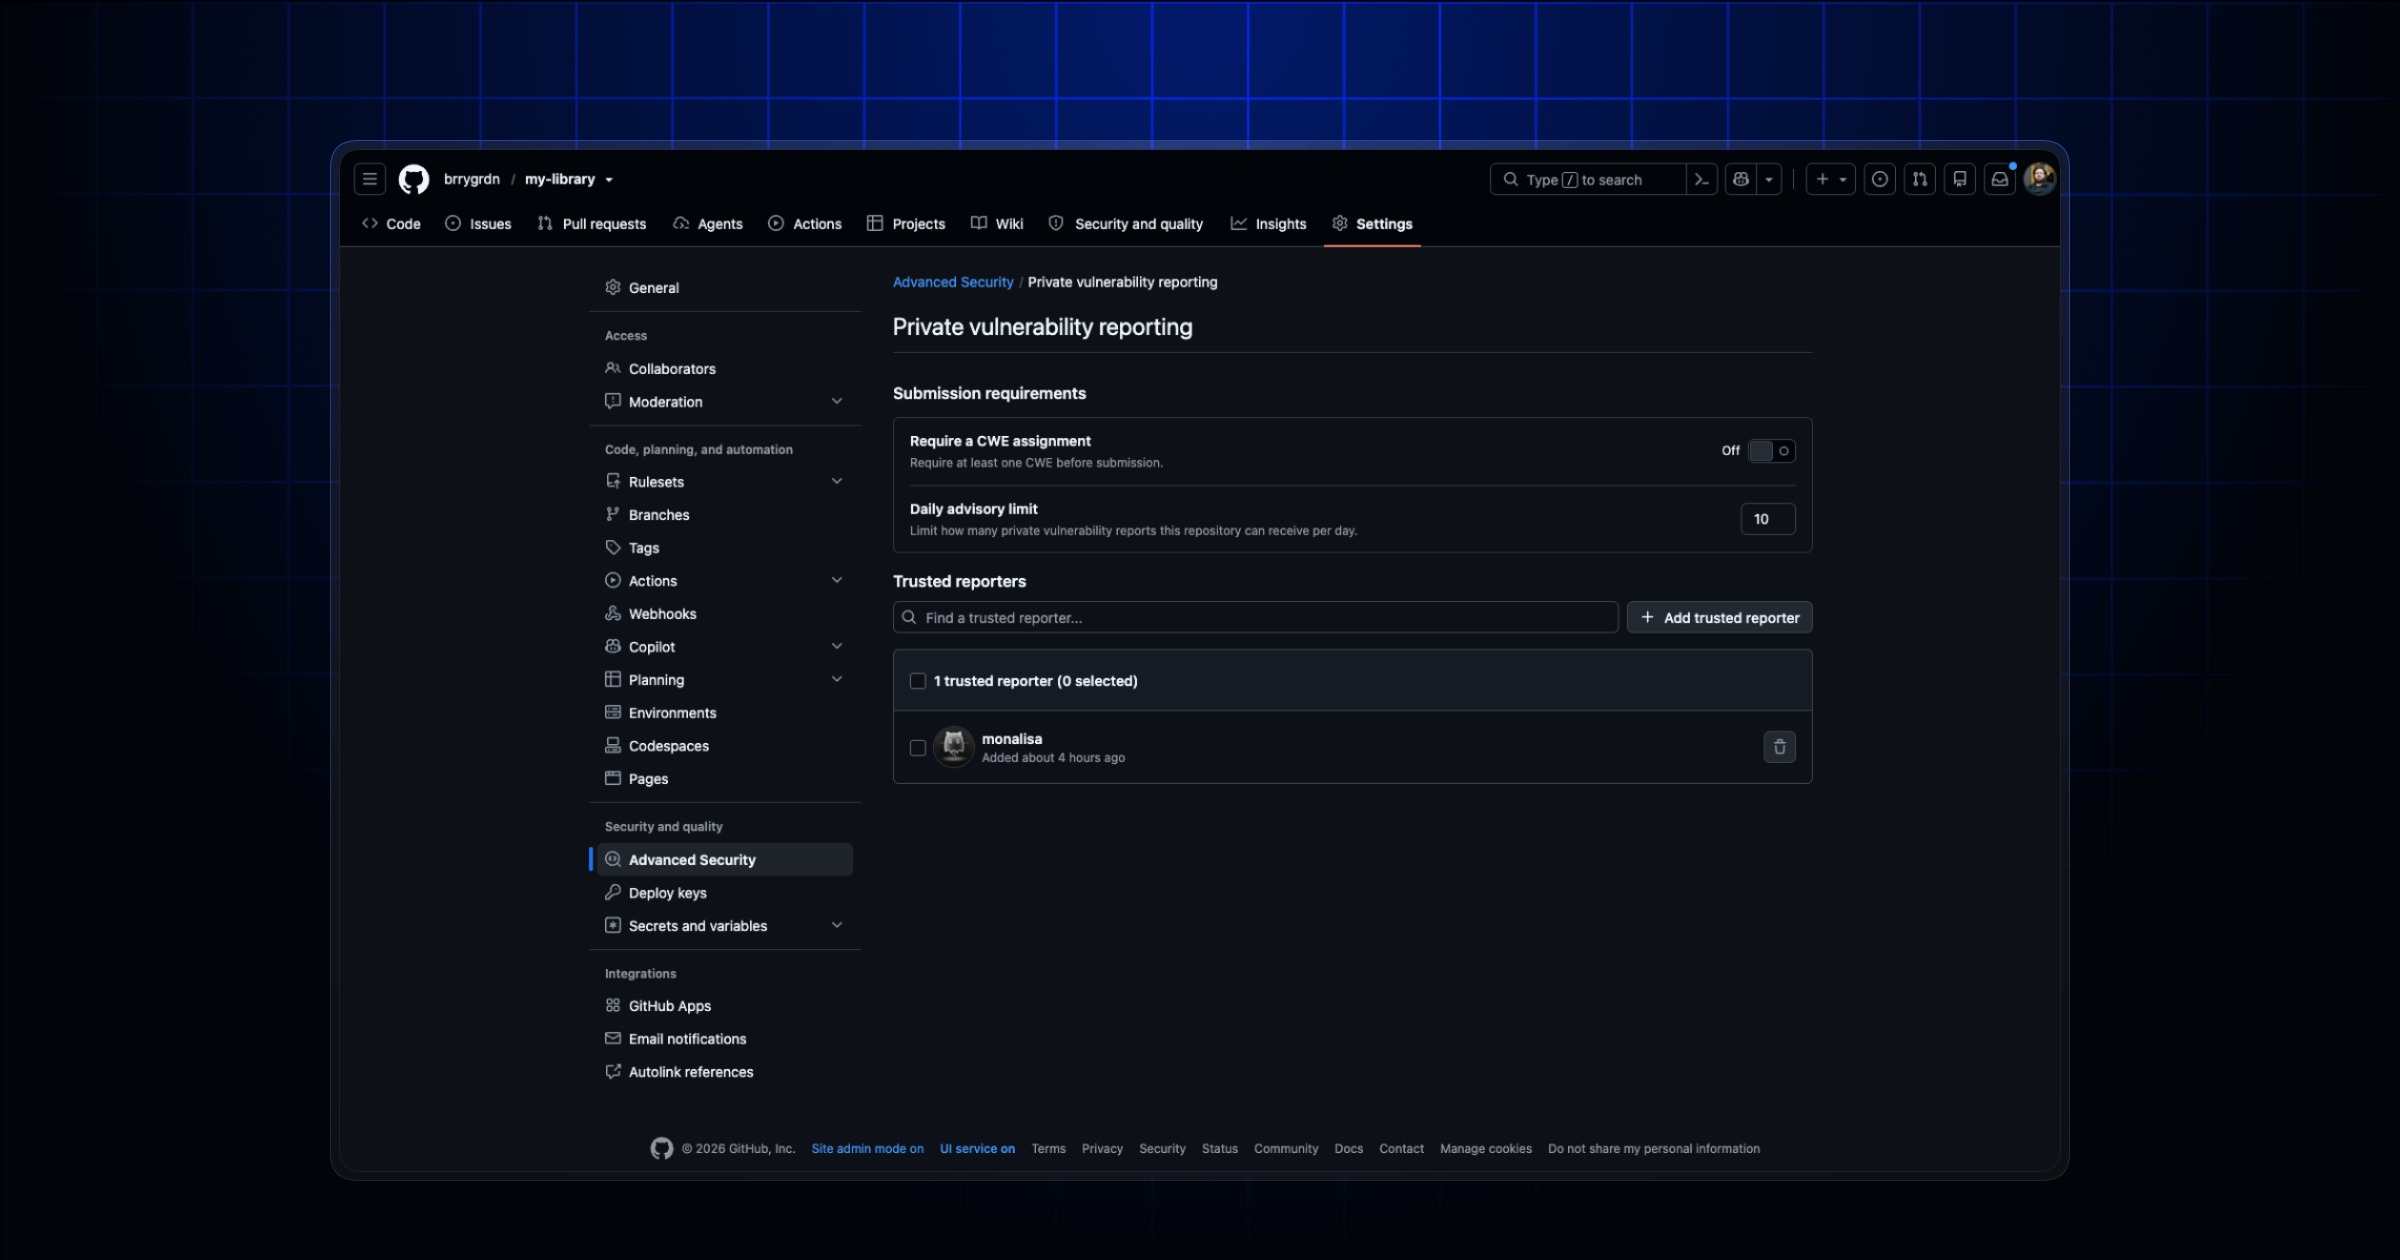
- Repo admins can set a daily overall cap
- Exemption
- Admins can allow-list trusted reporters
01What broke
GitHub launched a new rate-limiting feature designed to restrict the submission of private vulnerability reports on its platform. This release targets the growing problem of spam and automated submissions that target open-source repositories.
By introducing a cap on the number of new reports a single user account can submit within a given timeframe, the platform aims to reduce the noise generated by low-quality and automated security filings. Maintainers of open-source projects can now
Back to changelog Open source maintainers are receiving more low-quality and automated vulnerability reports, which can bury the reports that matter. Rate limits cap how many new reports a single account can submit in a day, both to your repository and across GitHub.
02Who is exposed
This helps protect you from bulk and automated submissions, while legitimate researchers can still reach you. With this update: Private vulnerability reporting now applies daily per-user rate limits to new reports.
Advertisement
Tech Pulse Daily
Get tomorrow's pulse first
Join engineers who read Tech Pulse before stand-up. Free, weekday mornings.
03What to do now
Reporters who reach a limit see a message asking them to try again later. See the full write-up from GitHub Changelog via the source link for quotes and complete context.
04How the issue works
Repository administrators can set a custom daily overall reporting limit for their repository. Repository administrators can add trusted reporters to an allow list so they’re never rate limited.
05What is still unknown about Rate limits for private vulnerability
Learn more in our docs about configuring private vulnerability reporting.

Author
Dillip Chowdary
Writes Tech Bytes coverage of AI, engineering, and the tools that actually ship. Editor of Tech Pulse Daily.
Related on Tech Bytes
Introducing Clef: our open-source decision models, and new RL fine-tuning platform
Read →
Microsoft AI models are now available on AI Gateway
Read →
Better Call GPT – Plugin for Talking to Claude Code in Live
Read →
Hermes ChatGPT Extension – Your Hermes Agents Inside Codex/ChatGPT
Read →
Today's Tech Pulse briefing
Full briefing →
Advertisement