Structured forms for private vulnerability reports
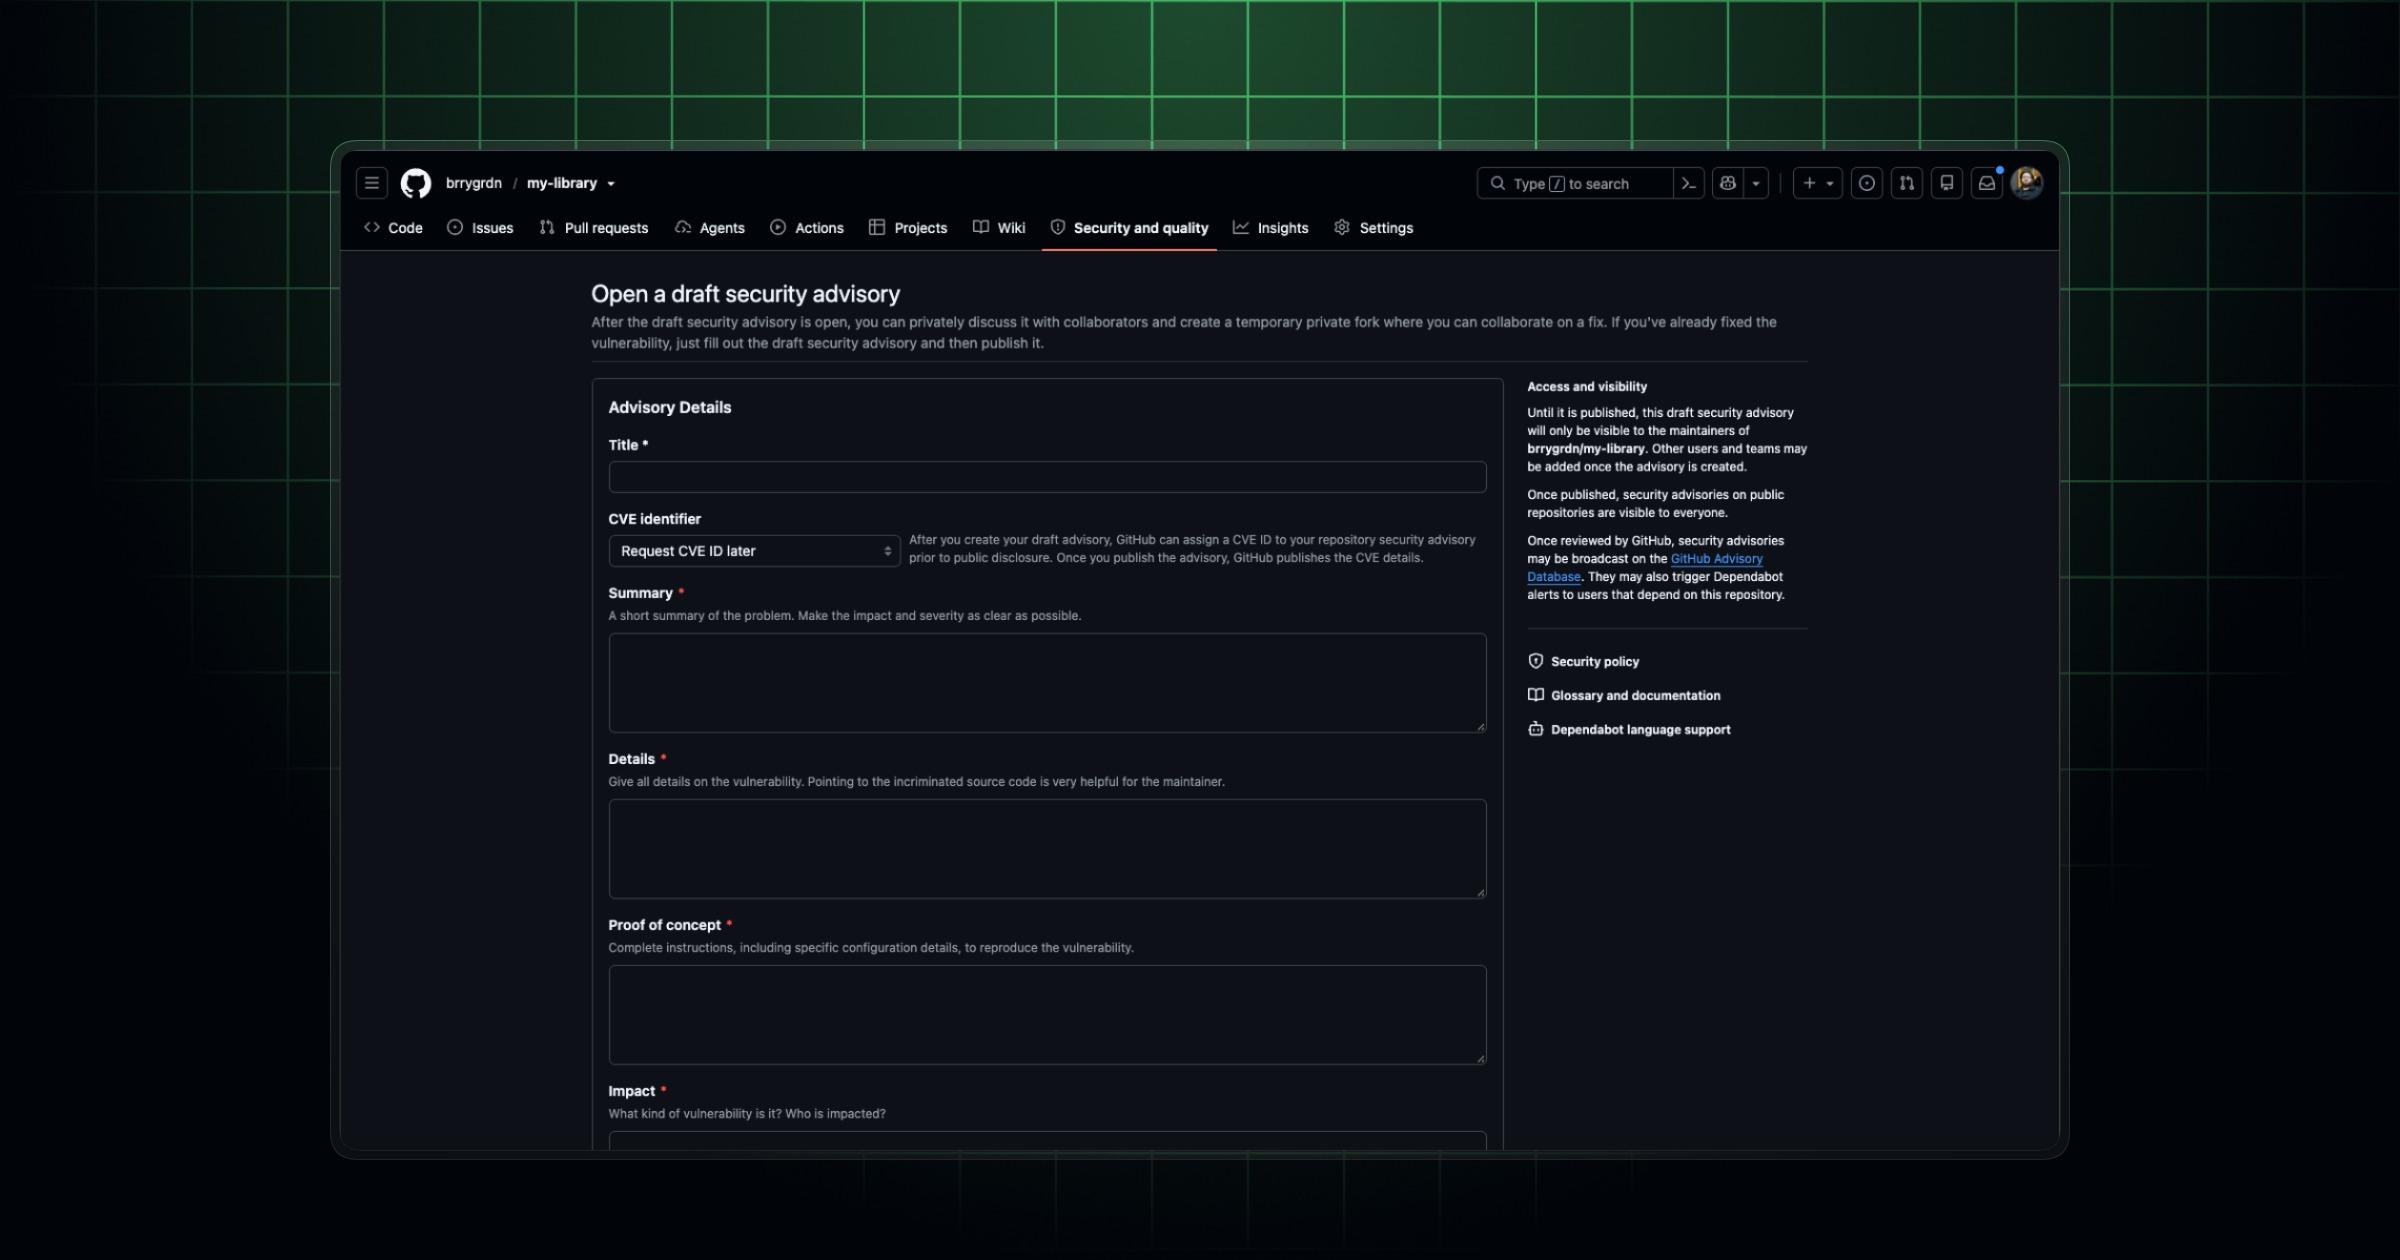
Private vulnerability reports can now use a structured form that asks reporters for the details you need to assess a vulnerability, including a reproducible.
By Dillip Chowdary • Oct 02, 2026 • Source: GitHub Changelog
What broke in Structured forms for private vulnerability
Advertisement
Tech Pulse Daily
Get tomorrow's pulse first
Join engineers who read Tech Pulse before stand-up. Free, weekday mornings.
5 real paragraphs? Yes, 2 intro + 10 section paragraphs = 12 total paragraphs. No bullet points? Yes, zero bullets. Verbatim Headings used? ## What broke in Structured forms for private vulnerability (Checked) ## Who is exposed by Structured forms for private vulnerability (Checked) * `
What to do now about Structured forms for private vulnerability
For primary quotes and complete technical detail, see GitHub Changelog's original report linked above.
Developer Action Items
- ☐ Diff the official changelog for GitHub before you bump — APIs, defaults, and removed flags only.
- ☐ Install through the vendor's documented channel in staging; keep a one-command rollback and time-box the canary.
- ☐ Grep your repo for old flag names, lockfile pins, and plugin versions that the notes mark as breaking.
- ☐ Prefer the first patch cut over the day-zero tag unless you have a reason to be on the leading edge.
- ☐ If GitHub Changelog did not name a region, plan, or SKU, screenshot the official availability line before you promise it to users.

Author
Dillip Chowdary
Writes Tech Bytes coverage of AI, engineering, and the tools that actually ship. Editor of Tech Pulse Daily.
Related on Tech Bytes
Audible announces AI-powered character guides, interactive stories, more
Read →
Steam Deck 2: Is AMD Gainsborough the chip Valve’s been waiting for?
Read →
Zero Trust Creator Says Model Holds Firm Against AI-Assisted Attacks
Read →
Twelve South launches tiny new ‘Airfly Drive’ wireless CarPlay adapter
Read →
Today's Tech Pulse briefing
Full briefing →
Advertisement