CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands
CTM360 uncovered over 1,000 scam campaigns impersonating brands like Amazon and Walmart to drive victims into paid subscriptions via fake gift cards.
By Dillip Chowdary • Nov 07, 2026 • Source: BleepingComputer
Digital risk protection provider CTM360 uncovered a massive global fraud operation on November 7, 2026, identifying over 1,000 active incidents where threat actors distribute deceptive gift card promotions. As detailed in BleepingComputer's report, these schemes lure consumers with fraudulent giveaways, bypass traditional credential harvesting, and systematically push victims through deceptive verification funnels that drive traffic to affiliate marketing offers and paid cellular subscriptions without ever delivering rewards.
This report examines the modular infrastructure, deceptive social media distribution methods, and automated affiliate tracking tokens that power these widespread brand impersonation campaigns. Designed for enterprise security teams and digital consumers alike, this analysis details how threat actors weaponize trusted corporate identities to generate unauthorized conversions, drain consumer mobile accounts through carrier billing, and evade standard domain blocklists.
CTM360 Exposes Fake Gift Card Scams: what actually changed
Threat intelligence researchers revealed a major strategic shift away from static phishing portals toward an industrialized, modular scam ecosystem built for rapid deployment. Rather than creating unique web assets for every target, operators established a standardized engine that separates visual brand assets from the core monetization backend. During ongoing tracking, analysts cataloged more than 1,000 incidents originating from this modular architecture. This technical flexibility allows attackers to swap impersonated corporate logos, modify celebrity lures, and register fresh domains in minutes without modifying their underlying conversion infrastructure.
The underlying monetization mechanics have also shifted away from conventional password theft and direct credit card harvesting toward commercial conversion funnels. Threat actors direct incoming victim traffic through dedicated affiliate tracking links containing customized tracking tokens. Instead of selling stolen credentials on illicit dark web markets, operators earn steady financial commissions directly through legitimate affiliate networks. By converting consumer clicks into verified application installations and mobile cellular subscriptions, threat actors build a recurring revenue stream while forcing commercial advertising platforms and telecommunications billing systems to handle transaction processing.
CTM360 Exposes Fake Gift Card Scams: how it works
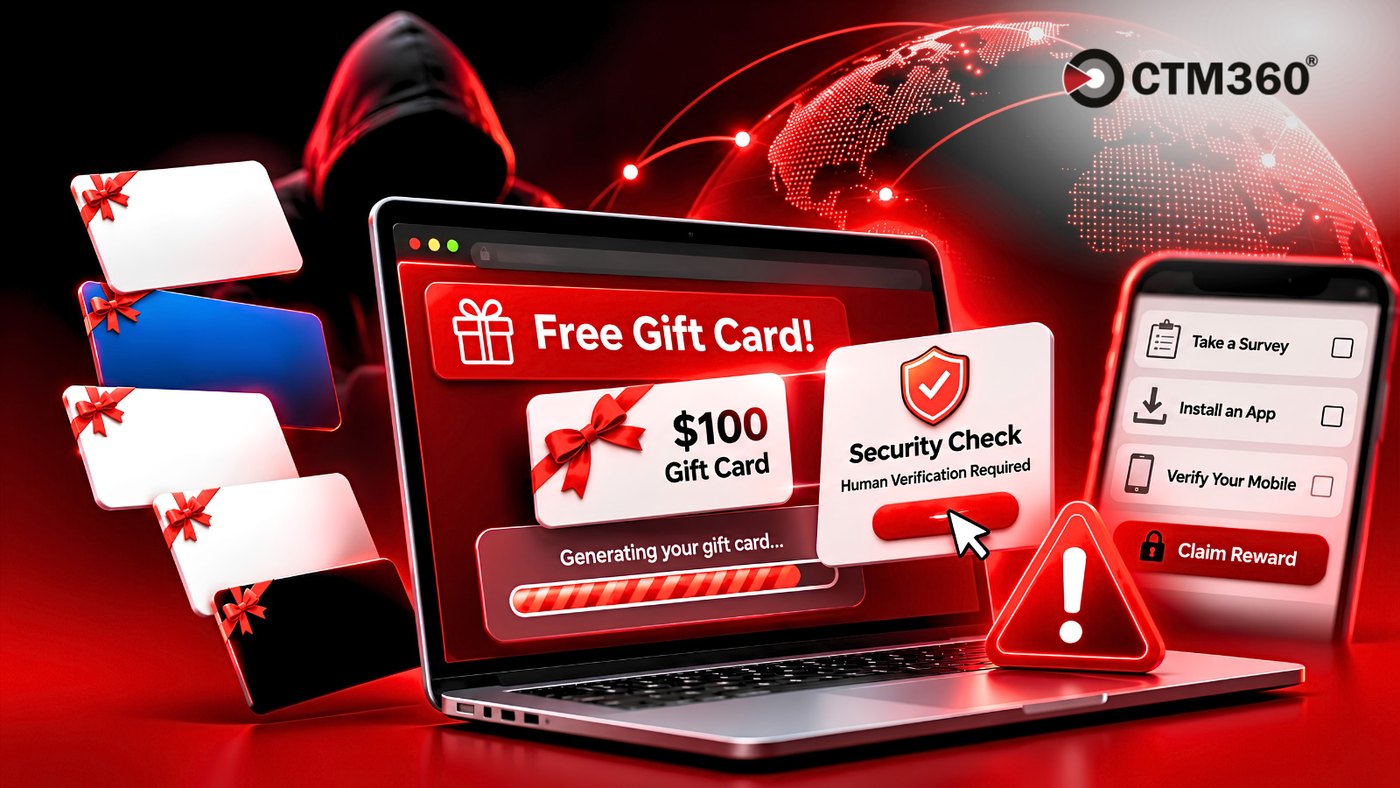
The fraudulent lifecycle begins on popular social media platforms where threat actors circulate sponsored advertisements and viral giveaway announcements. These promotions feature fabricated endorsements from prominent influencers like MrBeast and Alix Earle, promising complimentary account balances from reputable retailers. When a user clicks the promotional link, the browser loads a cloned portal displaying legitimate corporate colors, authentic logos, dynamic participant counters, live countdown timers, and fake testimonials from past winners. These visual elements combine to generate intense urgency and false credibility before the visitor selects a desired card denomination.
After the user picks a reward amount, the website executes a client-side animation that simulates backend code generation, displaying a partially masked string such as XXXX-XXXX-7F3A-XXXX to prove the card exists. The portal then presents a deceptive security gate designated as Trap 10, requiring human verification before releasing the final digits. This step redirects victims into an endless loop of surveys, browser extension installs, and mobile subscription pages demanding phone numbers and OTP confirmations. Destination URLs embed offer_id and aff_id tokens to credit attacker accounts, while the promised gift card is never delivered.
Advertisement
Tech Pulse Daily
Get tomorrow's pulse first
Join engineers who read Tech Pulse before stand-up. Free, weekday mornings.
CTM360 Exposes Fake Gift Card Scams: why it matters
This threat campaign represents an insidious evolution in cyber fraud because it operates almost entirely outside the defensive perimeter of targeted corporations. Because threat actors host these fake portals on independent infrastructure rather than compromising corporate servers, internal endpoint security tools and web application firewalls cannot detect the ongoing impersonation. Attackers weaponize brand reputation as an attack vector, exploiting consumer trust to harvest user data and generate affiliate revenue. The documentation of over 1,000 distinct incidents proves that affiliate-based social engineering has become a highly scalable, profitable commercial enterprise.
The campaign also exposes systemic vulnerabilities across mobile carrier billing ecosystems and global affiliate ad networks. When victims complete phone number submissions and verify incoming PIN or OTP codes, cellular operators automatically attach recurring monthly charges to the consumer phone bill. Affiliate marketing networks interpret these completed verification steps as legitimate consumer conversions, automatically dispensing commission payouts to the threat actors. This profitable monetization loop provides steady capital that attackers reinvest directly into sponsored social media ad placements, sustaining an automated cycle of digital brand abuse and consumer exploitation.
CTM360 Exposes Fake Gift Card Scams: who is affected
Individual consumers navigating social media feeds face immediate financial harm and widespread privacy loss from these fraudulent giveaways. Victims who fall for fabricated celebrity endorsements disclose valuable personal information, including full names, email addresses, and cellular numbers that are subsequently compiled into marketing databases and targeted spam distributions. More severely, users who complete the deceptive mobile verification prompts incur unexpected recurring subscription fees added to their monthly cellular statements. Those who follow instructions to download sponsored software risk compromising their personal computers or mobile devices with unwanted extensions and telemetry applications.
Established commercial enterprises endure extensive brand dilution and customer support friction caused by unauthorized corporate impersonation. The ongoing campaign systematically targets high-profile consumer brands, including Amazon, Walmart, PlayStation, Sephora, and SHEIN, mimicking their official logos and styling. When deceived consumers realize the promised rewards do not exist after completing intrusive offers or suffering carrier charges, their dissatisfaction and complaints fall squarely upon the legitimate retailers. Enterprise security and marketing teams must commit substantial time and financial resources to track, monitor, and remove these fraudulent third-party domains across the web.
CTM360 Exposes Fake Gift Card Scams: what to watch
Corporate security teams and threat intelligence professionals must maintain persistent surveillance over newly registered domains and external digital assets. Organizations need automated digital risk protection platforms to identify unauthorized uses of their corporate identity, trademarks, and partner associations across social media advertising registries. Because operators frequently cycle through temporary domain names and hosting providers to avoid security blocklists, defenders must look for shared architectural traits. These include simulated card generation scripts, live countdown timers, and telltale affiliate redirect parameters that expose the underlying infrastructure behind these fraudulent brand conversion networks.
Consumers must exercise extreme skepticism when encountering high-dollar promotional giveaways on social media feeds, particularly promotions citing endorsements from high-profile figures such as MrBeast or Alix Earle. Legitimate retailers never mandate that customers complete third-party surveys, install browser add-ons, or enter cellular verification codes to reveal a gift card. Any portal that displays a partially obscured promotional code and demands completion of external tasks should be recognized as an affiliate trap. Consumers should always cross-reference promotional claims on official company websites and regularly audit mobile phone invoices for unauthorized recurring subscription charges.
Developer Action Items
- ☐ Verify the claim on the official CTM360 Exposes Fake Gift page (or BleepingComputer), not from this recap alone.
- ☐ Name the surface that moved — API, policy, model, hardware, or commercial terms — before you Slack the thread.
- ☐ Assign one owner a day to read the primary material and decide: this-sprint, this-quarter, or noise.
- ☐ Do not change production on day-one coverage. Watch the vendor changelog and one independent write-up first.
CTM360 Exposes Fake Gift Card Scams FAQ
What brands are impersonated in these fake gift card scams?
Attackers impersonate major consumer platforms including Amazon, Walmart, PlayStation, Sephora, and SHEIN, using cloned brand logos, color schemes, and fake endorsements from figures like MrBeast and Alix Earle.
How does the fake gift card verification loop generate revenue?
Deceptive portals route users through affiliate tracking links with parameters like offer_id and aff_id. Threat actors earn commissions when victims complete surveys, install unwanted apps, or verify phone numbers for paid carrier-billed mobile subscriptions.
What is Trap 10 in the CTM360 gift card report?
Trap 10 describes the fraudulent human verification screen that appears after a fake card code is partially displayed. Instead of confirming identity, it redirects victims into an endless sequence of monetization tasks.
Do users ever receive a real gift card from these portals?
Across all test scenarios evaluated by CTM360 analysts, the portals continuously flagged completed steps as incomplete and never delivered an actual gift card code.
Sources

Author
Dillip Chowdary
Writes Tech Bytes coverage of AI, engineering, and the tools that actually ship. Editor of Tech Pulse Daily.
Related on Tech Bytes
Advertisement